Media Release
Police keep $465 million out of criminal hands by targeting Business Email Compromise scams
Editor’s note: ClickFit campaign material is available via Hightail.
Police have issued an urgent plea for vigilance against Business Email Compromise (BEC) as loss prevention and recovery figures under Operation Dolos head towards the half a billion-dollar mark.
Through Operation Dolos, the Joint Policing Cybercrime Coordination Centre (JPC3), state and territory police, and industry partners, work together to disrupt the growing threat of BEC and the criminal networks behind them.
The cybercrime operation, established in January 2020, has so far helped recover or prevent $465 million in losses from Australians and Australian businesses targeted by BEC activities.
According to the National Anti-Scam Centre's Targeting Scams Report, payment redirection scams – also known as Business Email Compromise – resulted in $166.8 million in reported losses last year, making it the second most costly scam type in Australia after investment scams.
The size and scope of the problem has prompted a new ClickFit campaign from the JPC3 to boost awareness and education in the wider community.
BEC unfolds when a cybercriminal impersonates a trusted business, supplier, executive or colleague to deceive and pressure clients, customers or employees into redirecting legitimate payments into fraudulent accounts they control.
The scam typically begins when the offender gains unlawful access to a victim’s emails and monitors the inbox for weeks, or even months, so they can build intelligence and identify upcoming payments which could be disrupted or stolen.
Offenders use ‘typosquatting’ to send payment requests from email addresses which closely mimic legitimate businesses and may delete emails or alter inbox rules to hide their activity.
Scammers often target high-value transactions including property settlements, building projects and supplier invoices, with victims left unaware they have been deceived until the intended recipient makes contact or advises they have not received any payment.
Perpetrators will use high-pressure tactics to prevent victims from verifying payment requests, frequently targeting them before weekends or public holidays, and claiming urgent action is needed to avoid penalties, project delays or missed deadlines.
By then it’s usually too late to cancel the transaction to the criminal’s account or too late for the victim’s bank to recover the funds.
AFP Detective Superintendent Marie Andersson laid down a warning to cybercriminals.
“Cybercriminals rely on people being rushed, distracted or pressured into making snap decisions. Our message is simple: Australians are becoming more aware of your tactics. Every time someone stops to verify a payment request, it becomes increasingly harder for these criminals to succeed,” Detective Superintendent Andersson said.
The reminder for vigilance against BEC aligns with the beginning of Cyber Security Action Month, a government initiative to promote online safety, data protection and secure digital habits.
“Business email compromise can be effective because it exploits trust, business operations and our daily digital routines,” Detective Superintendent Andersson added.
“Cybercriminals carefully impersonate legitimate businesses and employees by copying branding and communication styles and create a sense of urgency to pressure their victim into acting quickly before they have time to realise it’s a scam.
“The sad reality is that because this type of compromise is a business for criminals, and they have sophisticated techniques deceptive enough to target anyone involved in processing or approving payments, from CEOs to Mum or Dad invoicing at home.”
This is why it’s so important for people to educate themselves and to take a moment to safeguard and recognise these common warnings signs of BEC:
- Requests to change bank or payment details;
- Minor changes to email addresses or domains;
- Newly registered domains designed to resemble a legitimate business;
- Emails which appear genuine because they originate from a compromised account;
- Unsolicited follow-up calls confirming payment instructions;
- Unprompted MFA or device logins;
- Unfamiliar attachments or documents.
As part of the new ClickFit campaign focused on safety tips, Australians and Australian businesses are urged to follow six simple steps everyone can take before making a payment to help protect against cybercriminals.
Stop before you act
Pause before you action any invoice, email, payment request or bank detail changes. Criminals are counting on you to rush. Always double-check.
Check payment details carefully
Compare bank account details with previous invoices and be alert to changes in bank details, payment processes and email addresses.
Protect against impersonation
Watch for slight changes in email addresses or domains, unexpected emails, calls or shared documents, and unusual requests for payment.
Verify before making payment
Always verify payment or changes in bank account details using a trusted phone number or in-person. Never use contact details provided in the email.
Be alert to urgency
Be suspicious of urgent payment requests, demands for secrecy, or attempts to bypass normal approval processes. Criminals create pressure to stop you from checking.
Report immediately
If you have transferred money or something doesn’t feel right, call your bank via their official contact, notify your IT team and report it to police.
Case studies
In May, 2026, three people were charged as part of an investigation into an alleged $600,000 business email compromise scam, where criminals are accused of using fraudulently obtained funds to purchase large amounts of gold bullion.
The investigation, led by NSW Police Cybercrime Squad and supported by the AFP-led Joint Policing Cybercrime Coordination Centre (JPC3), identified suspicious transactions linked to a 20-year-old woman who allegedly bought $100,000 worth of gold on five occasions.
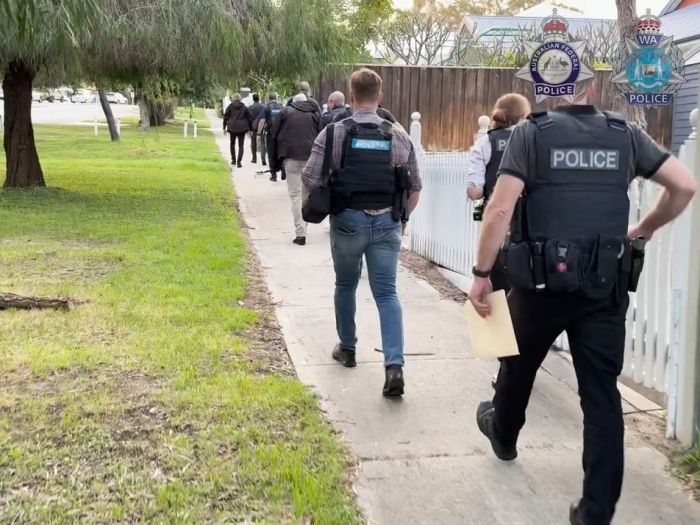
Police arrested a woman and two men, aged 29 and 36, in Sydney and seized cash, mobile phones, gold bullion and other evidence during searches.
All three were charged with offences including dealing with proceeds of crime, participating in a criminal group and, for the two men, identity related offences, with the matter proceeding before the courts.
Authorities recovered about $300,000 of the allegedly stolen funds, while investigations into the broader scam remain ongoing.
In July, 2025, a 38-year-old Sydney man was charged after allegedly helping deal with $3.5 million stolen through a business email compromise scam targeting the Northern Territory Government.
Police allege he registered a company with a name similar to a legitimate construction contractor and used fraudulent emails and bank details to trick the agency into sending more than $3.58 million to a bank account under his control.
The AFP investigation began after a bank reported the suspicious transaction, with inquiries allegedly linking the scheme to the man through a phone number provided on the fake vendor identification form.
He was arrested following a search of his home, where police seized electronic devices and company related documents, and has been charged with dealing with proceeds of crime worth $1 million or more.
The majority of the allegedly stolen money was recovered, although police allege the man accessed some of the funds before authorities intervened.
A Tasmanian couple nearing retirement had arranged a construction loan to build their home and paid regular instalments to their builder as work progressed.
After months of legitimate transactions, USA-based cybercriminals intercepted the process via email and sent a fraudulent invoice which appeared to come from the builder.
The invoice contained altered bank account details which went unnoticed and a $47,500 payment was made to the account controlled by the scammers.
The bank sent an email to the victim to clarify if the changed account details were correct, but this was intercepted by the scammers, so the victim remained unaware.
When a subsequent invoice arrived, the same situation played out, but the bank identified the discrepancy and notified the victim by phone. Further transactions were halted and the matter was reported to police.
Payments to the legitimate builder’s account had stopped so they discontinued work on the home, and the victims had to vacate their rental property.
A Victorian victim was arranging the purchase of a gravestone to honour their deceased mother. After emailing a company to arrange the purchase, a cybercriminal inserted a false invoice into the email chain.
The invoice was for $2300 and was paid by the estate of the deceased. The email and invoice appeared to be from the correct business, so the victim authorised the payment.
A Victorian person received an email from someone pretending to be his conveyancer, requesting a $45,000 deposit to be transferred for a property purchase.
The payment was transferred because the victim believed it was a genuine transaction due to the scammer knowing details such as the address and contact information. The victim only became aware he transferred the deposit to a scammer’s account when he spoke to his conveyancer by phone.